is it safe to give an outsourced bookkeeping firm access to my bank accounts and financial data
If you are asking, “is it safe to give an outsourced bookkeeping firm access to my bank accounts and financial data,” the practical answer is yes when access is limited, monitored, and separated from payment authority. A bookkeeper generally needs transaction data to reconcile accounts and prepare accurate reports, but not the ability to move money.
Key Takeaways
- The safest setup gives your bookkeeper read-only access to your bank feeds, so they can reconcile transactions and build your reports without ever having the power to move money.
- Never share your bank login credentials with an outside firm; use the bank's secure feed or an accounting integration that creates a separate, revocable connection.
- Build a simple review routine: check your bookkeeper's access quarterly, confirm your bank alerts are active, and revoke permissions the day the engagement ends.
- Before you sign, ask the firm about their internal security controls, encryption standards, and whether they carry professional liability insurance, then get the answers in writing.
- A well-structured bookkeeping relationship reduces your risk overall, because timely, accurate books mean you spot unauthorized transactions or errors early instead of months later.
The right setup gives your finance partner enough visibility to maintain clean records while you retain approval power. Cypher’s Bookkeeping service is designed around organized financial data, accrual-basis bookkeeping, and monthly financial statements. The framework below shows how to grant access without surrendering control.
Is Giving Your Bank Account Access to a Bookkeeper Really Safe? Let's Break It Down
Yes, provided the firm uses view-only permissions, secure bank feeds, multifactor authentication, and separated duties. A bookkeeping firm should not require your primary username, password, security answers, or unrestricted administrator access. You should retain authority over transfers, wires, new payees, check issuance, and final payment release.
The Founder's Dilemma: Trust vs. Control
Bank access is not an all-or-nothing decision. Reconciliation, categorization, cash reporting, and month-end close require transaction visibility. Sending funds, changing account settings, and adding beneficiaries require a separate approval path. Your bookkeeper can review deposits, withdrawals, fees, card activity, and transfers while you control the cash itself.
Why This Question Matters More Than Ever
Remote accounting connects bank portals, credit cards, payroll, payment processors, expense tools, and cloud accounting software. Poor connections lead to spreadsheets, emailed statements, and shared passwords, creating opportunities for missing transactions, duplicate entries, outdated permissions, or disclosure.
A disciplined access model also limits exposure to vendor records, customer payments, payroll information, tax documents, loan activity, and management reports. Ask for an access map before onboarding: connected systems, user permissions, activity reviewers, and the process for removing access.
Introducing the Zero-Trust Approach to Financial Data
Zero trust means no user, device, or application receives automatic trust. Access is granted for a defined purpose, limited to necessary permissions, and reviewed over time. For bookkeeping, this can mean a view-only bank user, a direct transaction feed, individual logins, multifactor authentication, and documented approval boundaries.
Your Zero-Trust Blueprint: Mastering Bank Access with View-Only Permissions
What Exactly Is “View-Only” Bank Access?
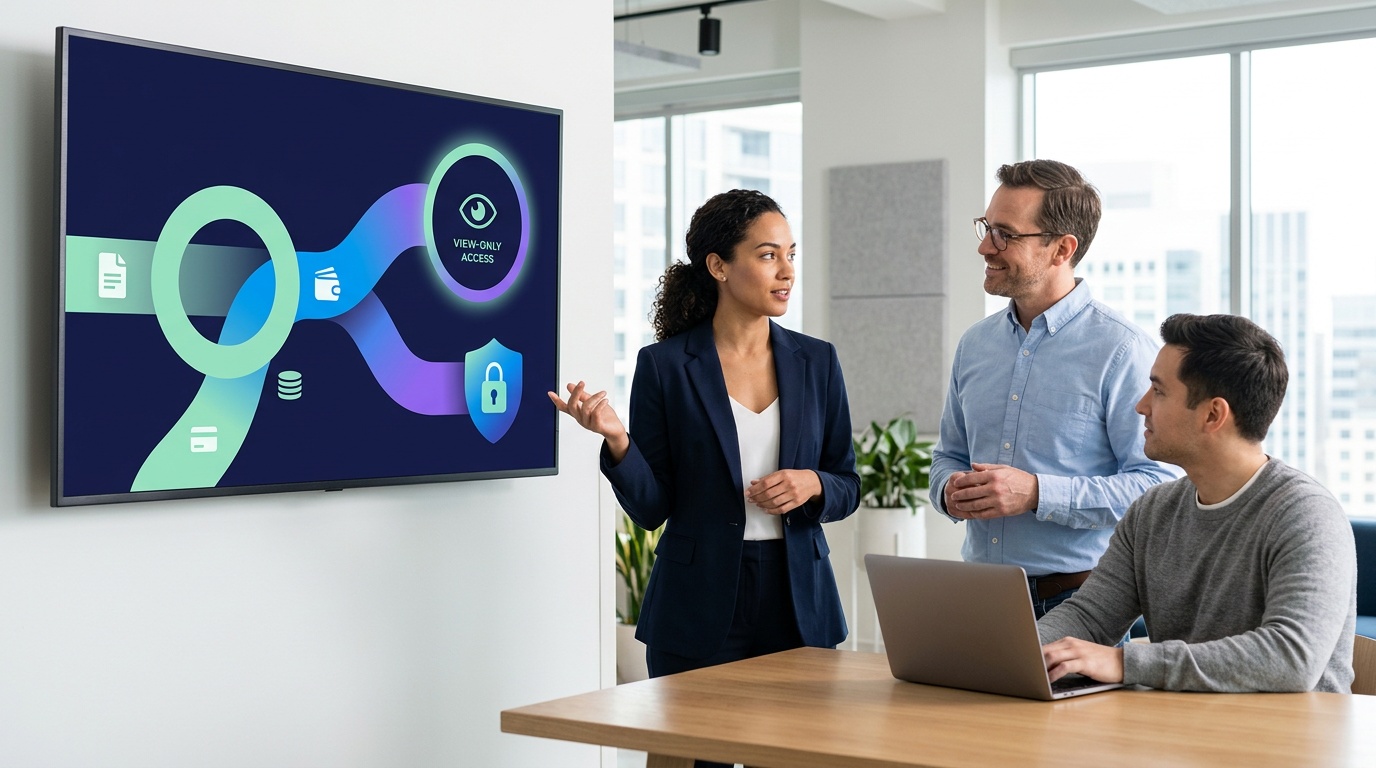
View-only access lets an authorized user review balances, transaction history, statements, and related details without initiating transfers or changing core controls. Roles differ by bank, so review the user-role description for restrictions on wires, ACH payments, bill pay, checks, external transfers, beneficiary changes, password changes, and user administration.
Do not share personal banking credentials. Use the bank’s secondary-user or delegated-access process, then confirm the permission set from the account owner’s dashboard. If the bank lacks a genuinely read-only role, a direct feed or statement workflow may be safer than broad credentials.
How to Configure View-Only Access in Major Banking Platforms
Bank menus differ, but the implementation sequence is consistent:
- Start with an access inventory. List checking, savings, credit-card, line-of-credit, payment-processor, and treasury accounts requiring reconciliation.
- Create an individual user. Invite the accounting professional through the institution’s user-management screen. Never create a shared login.
- Select the narrowest role. Choose inquiry, reporting, read-only, or similar permissions. Remove payment, transfer, user-management, and profile-editing rights.
- Require multifactor authentication. Each user should authenticate with an approved second factor tied to that individual.
- Test before full onboarding. Confirm that the user can view required activity but cannot access payment tools or modify security settings.
- Document and review. Record the role, accounts, owner, and review date. Recheck permissions when responsibilities change.
Why Reputable Firms Like Cypher Never Ask for Full Admin Credentials
Full administrator credentials combine unnecessary exposure with payment authority, make activity harder to attribute, and complicate offboarding. A professional workflow uses named users, least-privilege permissions, secure invitations, and an audit trail.
For Cypher’s Bookkeeping service, the goal is dependable financial information, not control over your cash. Ask which permissions are needed, which actions are prohibited, and how access is reviewed before making the connection.
Beyond View-Only: Understanding Other Secure Data Connections
A bank feed reduces manual downloads and moves transaction data into the accounting ledger. Options include an institution-supported aggregator, direct bank feed, or scheduled statement uploads. Review the connected application, data scope, refresh behavior, and revocation process before approval.
| Connection method | What it provides | Control questions to ask |
|---|---|---|
| View-only bank user | Balances, activity, and statements inside the bank portal | Can the user transfer funds, add payees, or edit account settings? |
| Direct bank feed | Automated transaction delivery to approved accounting software | Which accounts and fields are shared, and how is the feed disconnected? |
| Secure data aggregator | Permissioned connection between financial institutions and finance tools | Is the connection authorized by you, protected by multifactor authentication, and limited to needed data? |
| Statement upload | Periodic files for reconciliation when live feeds are unavailable | Are files transferred through an approved secure workspace rather than email? |
If transactions fail to sync, check connection status, date range, duplicate imports, account mapping, and feed permissions before sharing broader credentials. Use a controlled statement process temporarily, then reconcile the ledger after restoration.
The Dual Control System: Keeping Your Money Safe with Segregated Duties
The Pillars of Financial Security: Segregation of Duties Explained
Segregation of duties means no single person controls the full payment cycle. One person may enter a bill, another review support, and a separate authorized user release funds. This limits damage from error, compromised credentials, or intentional misuse while creating an audit trail tied to named users and defined responsibilities.
Your accounting partner can reconcile transactions, match invoices to vendors, code expenses, and prepare an accounts payable batch without unrestricted treasury authority. Document approval thresholds, payment types, vendor changes, and bank permissions before work begins.
How Outsourced AP Works: Drafting Payments Without Approval Power
The firm can receive invoices, check vendor details, confirm amounts and due dates, record liabilities, and prepare payment batches or draft instructions. The draft is not the release; it is a documented proposed transaction.
Establish rules for duplicate invoices, unusual bank details, missing support, new vendors, rush requests, and changed remittance instructions. Verify vendor changes independently through a known contact method.
Founder's Role: The Final Payment Release Authority
The founder or designated internal approver should retain final release authority. Review the payee, amount, invoice, cash position, payment date, and exceptions inside the bank or payment platform using an individual login and multifactor authentication. Backup approvers, dollar thresholds, and scheduled payment runs can preserve separation between preparation and authorization.
Preventing Fraud: Why This Two-Step Process Is Non-Negotiable
Dual control addresses stolen credentials, altered invoices, social engineering, urgent-payment pressure, and human error. Separate preparation and authorization create a second point at which a transaction can be questioned before cash leaves the account.
What Happens When Transactions Don't Sync Cleanly?
A failed bank feed should trigger a controlled exception process, not broader credentials. Determine whether the issue involves an expired connection, missing account, duplicate import, incorrect date range, mapping problem, or delayed transaction. Preserve statements and supporting records, document the affected period, and use an approved secure statement workflow until the feed is repaired. Reconcile temporary records afterward, checking for duplicates and omissions.
Vetting Your Partner: How to Ensure Your Outsourced Bookkeeper Is Trustworthy
Beyond the Sales Pitch: Essential Security Questions to Ask
Ask who receives bank-data access, whether users have individual accounts, which permissions are required, and how changes are approved and recorded. Ask how the firm handles suspicious invoices, compromised credentials, lost devices, staff turnover, and an unavailable approver.
Request a system map covering banks, credit cards, payroll, payment processors, expense tools, and cloud accounting software. Identify shared data, storage locations, data movement, export rights, and approved secure workspaces.
What to Look For: Credentials, Insurance, and Processes
Evaluate experience with your business model, accounting basis, transaction volume, and reporting needs. Ask whether the engagement includes accrual-basis bookkeeping, monthly financial statements, reconciliations, close procedures, accounts payable support, and tax-ready accounting coordinated with qualified tax partners. Cypher’s Bookkeeping service is one example of an outsourced accounting offering built around recurring records and reporting.
Request applicable professional liability or cyber insurance, written security policies, confidentiality requirements, background-screening practices if used, and an incident-response process. Certifications and insurance do not replace permission design; evaluate people, procedures, technology, oversight, and contractual accountability together.
The Importance of NDAs and Service Agreements
The service agreement should define services, systems, approved users, data ownership, confidentiality, security expectations, reporting cadence, payment responsibilities, and incident notification. It should state who may authorize payments or change vendors and bank instructions. Ask how records are returned, retained, or destroyed when the relationship ends.
Understanding Cloud Accounting Security Standards: SOC 2, Encryption, and MFA
SOC 2 reports should be reviewed for scope, system boundaries, reporting period, and tested controls. Encryption protects data during transmission and storage, while multifactor authentication adds verification beyond a password. Ask whether MFA applies to every user, administrator rights are restricted, devices are managed, and logs are reviewed.
Confirm that sensitive files use an approved secure workspace rather than personal email or unprotected links. Evaluate Cypher’s Bookkeeping service through the same questions: access scope, user accountability, data handling, and review procedures.
Offboarding Protocols: Ensuring Access Is Revoked Securely
List every bank role, accounting user, feed, workspace, password-manager entry, payment-platform permission, and connected application. Remove users, revoke sessions and tokens where supported, rotate shared secrets, and confirm that no former user remains an administrator. Request written confirmation, review recent bank activity and vendor changes, and verify connected applications after termination.
- Named users and least-privilege permissions are required.
- Payment preparation and payment approval are assigned to different people.
- MFA, encryption practices, incident response, and audit logging are explained clearly.
- Confidentiality, data ownership, retention, and offboarding terms appear in writing.
- Access is reviewed periodically and revoked promptly when responsibilities change.
From Chaos to Clarity: Reclaiming Your Books Securely
Addressing the “Messy Books” Pain Point: A Secure Recovery Path
Falling behind on bookkeeping is a recovery project. Define affected periods, accounts, missing statements, unreconciled transactions, and reporting decisions that depend on reliable numbers. Use a controlled document workspace, named users, and a written access plan. The safety of outsourced access depends on engagement controls, not on remote work itself.
How Cypher Reconciles Backlogs Without Compromising Security
Cypher’s Bookkeeping service can be evaluated as a path from incomplete records to dependable reporting. Cleanup may include account inventory, opening-balance review, bank and credit-card reconciliations, transaction classification, duplicate detection, missing-document follow-up, and period-by-period close procedures. Access remains limited to needed systems; payment authority, user administration, and cash-release decisions stay separate.
The Benefits of Accurate, Cleaned-Up Financial Data
Clean records provide a usable view of cash, receivables, obligations, recurring expenses, gross margin, and operating performance. They support monthly financial statements, budgets, forecasts, board reporting, fundraising preparation, and tax-ready accounting coordinated with qualified tax partners. Complete, properly classified transactions help leadership distinguish timing issues from real performance changes.
Gaining Peace of Mind and Strategic Financial Clarity
A recovery plan should end with a repeatable close calendar, assigned responsibilities, exception tracking, and a review of connected systems. Cypher’s Bookkeeping offering includes accrual-basis bookkeeping and monthly financial statements, subject to current service scope. The goal is current records, protected data, and founder decisions based on reliable information.
Frequently Asked Questions
Should I give my bookkeeper access to my bank account?
Giving a bookkeeper access to your bank account can be safe when access is limited to viewing transactions and statements. Use a named secondary user, multifactor authentication, and the narrowest available role, while keeping transfers, payee changes, wires, and payment approvals under your control.
What is the most secure online bookkeeping service?
The most secure online bookkeeping service is one that uses least-privilege access, individual logins, multifactor authentication, secure data connections, and documented offboarding. Ask how the firm protects financial data, reviews permissions, separates bookkeeping from payment authority, and handles access when a team member or engagement changes.
What does an outsourced bookkeeper do?
An outsourced bookkeeper organizes transaction data, reconciles accounts, categorizes activity, and prepares financial reports for your business. Depending on the agreed scope, an outsourced bookkeeper may also support month-end close, accounting software integrations, and accounts payable or receivable processes without receiving authority to move company funds.
Is it safe to connect your bank account to QuickBooks?
Connecting your bank account to QuickBooks can be safe when you approve the correct accounts, review the connection scope, and use secure login and multifactor authentication practices. A bank feed usually imports transaction data for accounting, but business owners should still monitor connected apps, reconcile activity, and revoke access when it is no longer needed.
Why don't accountants like QuickBooks?
Accountants generally use QuickBooks when its setup, account structure, integrations, and transaction data fit the business, so the concern is usually poor configuration rather than QuickBooks itself. Problems can arise from duplicate feeds, uncategorized transactions, incorrect account mapping, weak access controls, or relying on software without a consistent month-end review.
How can I protect financial data when hiring an outsourced bookkeeping firm?
Protecting financial data starts with an access map that lists connected banks, cards, payment processors, accounting tools, permissions, and review dates. Use separate user accounts, view-only bank roles or approved data feeds, multifactor authentication, and a written offboarding process, while keeping payment release and account administration with authorized company leaders.
